CYBER FRI (Analyst Edition) — Sept 18, 2026
Yasmine Johnston-Ison
A deeper cut for the threat intel analysts and security leads who want the technical details behind this week's headlines. Three stories, full IOCs, and what they mean for the deal table.
1. Cisco Identity Services Engine — actively exploited zero-day (CVSS 10.0)
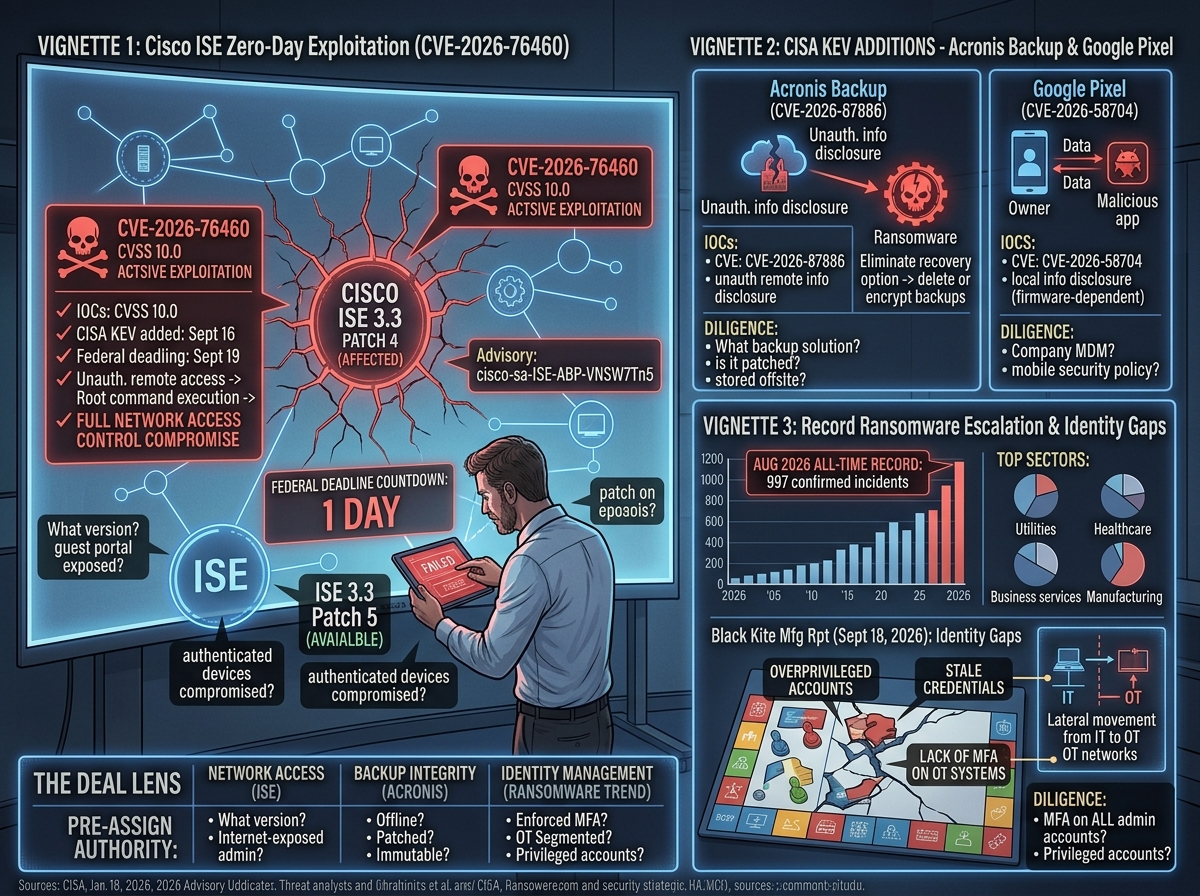
The vulnerability: CVE-2026-76460 — an unauthenticated remote code execution flaw in Cisco Identity Services Engine (ISE). CVSS 10.0 (maximum severity). The flaw allows an attacker to execute arbitrary commands on the underlying operating system with root privileges without any credentials.
Affected versions: Cisco ISE 3.3 Patch 4 and earlier; ISE 3.2 Patch 7 and earlier; ISE 3.1 Patch 6 and earlier.
Exploitation status: Cisco confirmed active exploitation in the wild. CISA added CVE-2026-76460 to the Known Exploited Vulnerabilities (KEV) catalog on September 16, 2026. Federal agencies have a patch deadline of September 19, 2026.
Patches available:
- ISE 3.3 → Patch 5
- ISE 3.2 → Patch 8
- ISE 3.1 → Patch 7
IOCs:
- CVE: CVE-2026-76460
- CVSS: 10.0
- CISA KEV added: September 16, 2026
- Federal patch deadline: September 19, 2026
- Attack vector: Unauthenticated remote exploitation
- Impact: Root-level OS command execution → full network access control compromise
- Advisory: Cisco Security Advisory cisco-sa-ISE-ABP-VNSW7Tn5
Why it matters for M&A: Cisco ISE manages who gets on the network. If your acquisition target runs ISE and hasn't patched, every authenticated device, every VPN session, and every guest access policy is potentially compromised. During diligence, ask: What version of ISE? When was it last patched? Who has admin access? Is there a guest portal exposed to the internet?
2. CISA KEV additions — Acronis Backup & Google Pixel (September 16)
Acronis Backup (CVE-2026-87886)
The vulnerability: An unauthenticated sensitive information disclosure flaw in Acronis Cyber Backup. Allows remote attackers to access sensitive system information without authentication.
IOCs:
- CVE: CVE-2026-87886
- CISA KEV added: September 16, 2026
- Attack vector: Unauthenticated remote information disclosure
- Product: Acronis Cyber Backup (multiple versions)
Why it matters for M&A: Acronis is the backup solution used by thousands of SMBs and MSPs. If the backup platform is compromised, ransomware attackers can delete or encrypt backups before deploying the payload — eliminating the recovery option. During diligence: What backup solution is in place? Is it patched? Are backups stored offsite or offline? Who has administrative access to the backup console?
Google Pixel (CVE-2026-58704)
The vulnerability: A local information disclosure vulnerability affecting Google Pixel devices. Requires local access or a malicious app already installed on the device.
IOCs:
- CVE: CVE-2026-58704
- CISA KEV added: September 16, 2026
- Attack vector: Local exploitation (requires device access or malicious app)
- Product: Google Pixel (specific firmware versions)
Why it matters for M&A: Most diligence checklists don't ask about mobile device security. But in small businesses where the owner's phone has access to email, banking apps, and sometimes the CRM, a compromised Pixel is a direct path to the company's most sensitive data. During diligence: Are company devices enrolled in MDM? Is there a mobile security policy? Does the owner's phone have access to business-critical accounts?
3. Record 997 ransomware attacks in August 2026
The numbers: Global ransomware attacks hit an all-time monthly record of 997 confirmed incidents in August 2026. This surpasses the previous record and represents a significant escalation from monthly averages in 2025.
Hardest-hit sectors:
- Utilities (power, water, energy infrastructure)
- Healthcare (hospitals, clinics, health tech)
- Business services (professional services, consulting, MSPs)
- Manufacturing (production lines, supply chain)
Key trend: A September 18 report from Black Kite found that manufacturing companies are disproportionately vulnerable due to identity management failures — specifically, overprivileged accounts, stale credentials, and lack of MFA on operational technology (OT) systems. These are the exact gaps ransomware groups exploit to move laterally from IT to OT networks.
IOCs & patterns:
- Attack volume: 997 confirmed incidents (August 2026)
- Top sectors targeted: Utilities, Healthcare, Business Services, Manufacturing
- Primary initial access vectors: Phishing, unpatched VPN appliances, compromised credentials
- Identity management gaps: Overprivileged accounts, stale credentials, missing MFA on OT systems
- Report source: Black Kite Manufacturing Cybersecurity Report (September 18, 2026)
Why it matters for M&A: If your target is in utilities, healthcare, or manufacturing, the ransomware risk isn't theoretical — it's statistical. The Black Kite report identifies identity management as the weakest link. During diligence: How many privileged accounts exist? When were credentials last rotated? Is MFA enforced on all admin accounts? Are IT and OT networks segmented?
The deal lens
This week's three signals map to three diligence checks every buyer should run before close:
- Network access control (Cisco ISE) — What version? Is it patched? Is the admin portal internet-exposed?
- Backup integrity (Acronis) — What's the backup solution? Is it patched? Are backups offline or immutable?
- Identity management (ransomware trend) — How many privileged accounts? Is MFA enforced? Are IT and OT networks segmented?
The businesses getting hit are in the sectors searchers buy. The gaps attackers exploit — unpatched systems, weak identity management, no MFA — are the same gaps that turn a good acquisition into a post-close crisis.
Sources:
- Cisco Security Advisory: cisco-sa-ISE-ABP-VNSW7Tn5
- CISA KEV Catalog (September 16, 2026)
- BleepingComputer: Cisco ISE zero-day exploitation report
- Industrial Cyber: Global ransomware attacks hit record 997 in August 2026
- Cybersecurity Dive: Manufacturing cybersecurity weaknesses report (Black Kite, September 18, 2026)
#CyberSecurity #ThreatIntel #IndicatorsOfCompromise #SMBAcquisition #DueDiligence #VulnerabilityManagement
Need Structured Guidance for Your Acquisition?
Book a 45-minute strategy call with our team to discuss your search progress, deal thesis, or transition plans.
Book an Appointment45 minutes to confirm fit and define next steps.
Related Insights
The Cyber Liabilities You Inherit on Closing Day
Unpatched firewalls, exploited Windows flaws, and open SaaS guest access do not appear in the P&L—but buyers inherit them at close.
CYBER FRI - Sept 11, 2026
Microsoft dropped 974 patches, CISA added 6 new exploits, and a new attack kit chains Windows + Chrome zero-days.